
Saphira AI

Rate this Tool
Average Score
Total Votes
Select your score (1-10):
Detail Information
What
Saphira is an AI-based product safety and cybersecurity compliance platform for engineering teams building certifiable machines, vehicles, and components. Based on the page, it is designed for organizations working against standards such as ISO 26262, IEC 61508, ISO 13849, ISO 10218, ISO 21434, UN R155, UL 508A, and IEC 61010.
Its core workflow is to ingest system design, requirements, test, calculation, and related engineering data, then generate analyses such as HARA, TARA, FMEA, safety cases, and cybersecurity cases while identifying missing evidence and traceability gaps. The positioning appears to be an enterprise-focused certification readiness and compliance intelligence layer that sits across existing engineering tools rather than replacing them.
Features
- Automated HARA, TARA, and FMEA generation — Generates risk and failure analyses from system design documentation to reduce manual review effort and improve consistency.
- Standards gap detection — Shows what is missing against specific safety or cybersecurity standards so teams can address issues before formal certification review.
- Safety and cybersecurity case generation — Produces structured documentation for certification workflows, helping teams prepare evidence for audits and assessors.
- Cross-tool traceability — Links requirements, design artifacts, code, tests, simulations, and models to expose fulfillment gaps and change impacts.
- Centralized compliance data aggregation — Ingests norms, requirements, tests, calculations, and files from multiple sources so evidence is not scattered across teams.
- Continuous monitoring and coverage reporting — Surfaces compliance gaps, incomplete requirements, and test coverage issues as designs evolve across releases.
Helpful Tips
- Evaluate this type of platform based on the quality of its traceability model, since certification delays often come from weak links between requirements, design, tests, and evidence rather than from document generation alone.
- Confirm which standards, artifact types, and engineering data sources are supported in your workflow; the page lists many standards, but implementation depth for each may vary by use case.
- Plan adoption around one certification bottleneck first, such as FMEA generation, test coverage reporting, or evidence collation, before expanding to broader safety and cybersecurity workflows.
- Treat AI-generated analyses as acceleration tools that still need domain expert review, especially for safety-critical and regulated product decisions.
- If your teams already use multiple engineering systems, prioritize governance for naming, versioning, and change management so centralized compliance views remain reliable.
Embed Code
Share this AI tool on your website or blog by copying and pasting the code below. The embedded widget will automatically update with the latest information.
<iframe src="https://aimyflow.com/ai/saphira-ai/embed" width="100%" height="400" frameborder="0"></iframe>
Explore Similar Tools
truthsystems
Truth Systems is a programmatic AI governance and unified compliance agent that helps organizations, especially legal teams and innovation leaders, monitor and block non-compliant AI use in real time across vendors through a browser extension and platform. For compliance, legal, and risk professionals, it can make AI oversight more actionable by embedding live guardrails, access controls, and audit trails directly into everyday work.
Variance
Variance is an AI risk intelligence platform that helps enterprises detect, investigate, and enforce against fraud, user-generated content violations, marketplace abuse, and other trust and safety risks, mainly for teams in content platforms, marketplaces, and financial services. For trust and safety, fraud, compliance, and security teams, it can speed real-time investigations and policy enforcement by connecting data streams and automating decisions across large volumes of activity.
Home | Veria Labs
Veria Labs is an AI-powered continuous pentesting platform that analyzes codebases and CI/CD workflows to find, validate, and suggest fixes for real application vulnerabilities, mainly for security and engineering teams in high-stakes industries. For AppSec, security engineers, and developers, it can bring offensive security testing closer to every pull request so issues are identified and remediated earlier in the software delivery process.
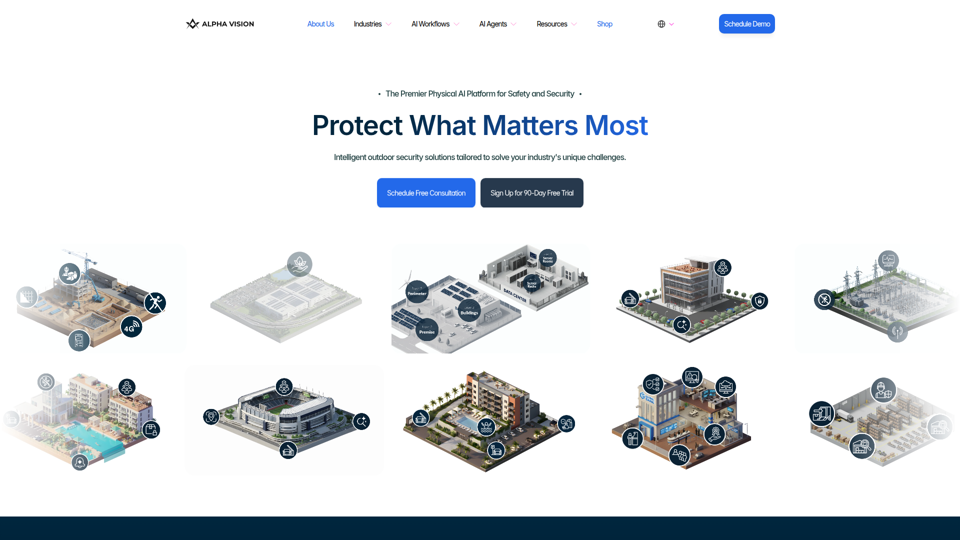
Premier Physical AI Security Platform & Outdoor Solutions | Alpha Vision | Free Trial
Alpha Vision is a physical AI security platform that uses AI agents and workflows to monitor outdoor sites, detect unsafe or unauthorized activity, deter trespassing, and search footage, mainly for security, safety, and operations teams in industries such as construction, education, retail, utilities, and commercial real estate. In AI-enabled security operations, it can help site managers, investigators, and safety leaders respond faster, review incidents more efficiently, and maintain broader coverage across large or distributed properties.
Autonomous AI Pentesting Platform | Maced AI
Maced AI is an autonomous AI penetration testing platform that helps engineering and security teams find, validate, and fix vulnerabilities across code, APIs, web apps, cloud, and infrastructure, while producing audit-ready reports for SOC 2 and ISO 27001 workflows. For security engineers, DevSecOps teams, and compliance-focused developers, it can shorten remediation cycles by turning validated findings into proof-of-exploit evidence and merge-ready fix guidance.
Mnemom — Prove What Your AI Agents Are Thinking
Mnemom is an AI governance and trust infrastructure platform that helps organizations prove, enforce, and audit what AI agents did and why with cryptographic verification, mainly for enterprise security, compliance, and engineering teams. For CISOs, compliance leaders, and AI platform teams, it can strengthen agent oversight by enabling pre-action policy enforcement and audit-ready evidence instead of relying only on after-the-fact logs.
Clearly AI
Clearly AI is an AI security and privacy review platform that automates threat modeling, design reviews, and risk triage to help security, privacy, and product teams ship software faster with better review coverage. In AI-assisted software delivery, it helps application security and privacy professionals focus human judgment on prioritized findings instead of repetitive document analysis and manual questionnaires.
Clone Detector – Brand Protection & Phishing Site Detection Tool
Clone Detector is a brand protection and phishing site detection tool that helps businesses and security teams find fraudulent domain clones and lookalike websites using domain fuzzing, visual similarity analysis, and risk-based reporting. For cybersecurity, compliance, and brand protection roles, it can improve AI-era monitoring by surfacing subtle impersonation threats earlier and supporting faster investigation, reporting, and response.