
Polymer Runtime Data Security | Secure AI Workflows
Rate this Tool
Average Score
Total Votes
Select your score (1-10):
Detail Information
What
Polymer is a runtime data security platform for AI and SaaS environments. It is positioned to help enterprises identify, analyze, and mitigate real-time security risks when data is generated, accessed, or moved by both employees and AI agents.
The product appears aimed at security, compliance, and IT teams that need stronger control over sensitive data across business applications and emerging AI workflows. Its core workflow combines identity-aware access management, data detection and classification, risk scoring, runtime policy enforcement, and audit logging for ongoing compliance visibility.
Features
- Identity-aware access controls: Groups human and non-human identities so organizations can manage how employees and AI systems interact with sensitive data.
- Data detection, classification, and labeling: Continuously monitors data in motion and at rest according to custom security policies, helping teams find and categorize sensitive information.
- Risk quantification and reporting: Produces reports and risk scores to surface issues such as shadow AI usage, insider threats, and configuration weaknesses.
- Runtime policy enforcement: Responds to violations in real time by redacting sensitive data, revoking file access, or triggering custom workflows with or without human review.
- Security operations support for end users: Includes real-time training and response mechanisms intended to involve employees in reducing security risk without fully blocking work.
- Continuous compliance evidence: Generates audit logs mapped to frameworks and regulations named on the page, including HIPAA, SOC 2, CCPA, and GDPR.
Helpful Tips
- Verify deployment fit early: The page mentions cloud and self-hosted single-tenant deployment, so buyers should map this against internal hosting, data residency, and operational requirements.
- Assess policy design maturity: Products like this are most effective when teams already know which data types, identities, and workflows need differentiated controls.
- Test human and AI identity coverage: Since Polymer emphasizes both employee and non-human access, implementation planning should confirm how AI agents, service accounts, and user groups are modeled.
- Prioritize high-risk workflows first: Start with sensitive SaaS and AI use cases where runtime redaction, access revocation, or workflow triggers would deliver the clearest risk reduction.
- Review evidence for ecosystem breadth: The page states that Polymer integrates with existing tools, but it does not list specific integrations here, so technical validation would be important during evaluation.
OpenClaw Skills
Polymer could likely pair well with OpenClaw as a control and response layer inside AI-heavy enterprise workflows. Likely OpenClaw skills could include data classification assistants, policy triage agents, compliance evidence collectors, and incident-response workflows that read Polymer alerts, summarize risk context, and route actions to the right teams. The page does not confirm a native OpenClaw integration, so this should be treated as a likely workflow pattern rather than a stated product feature.
In practice, that combination could help security and compliance teams move from passive monitoring to more adaptive runtime governance. For example, an OpenClaw agent could likely review Polymer-generated audit logs, assemble investigation summaries for shadow AI or insider-risk events, and trigger downstream remediation or employee guidance workflows. For regulated industries such as healthcare and financial services, this kind of pairing could reduce manual review effort while keeping AI adoption aligned with data handling policies.
Embed Code
Share this AI tool on your website or blog by copying and pasting the code below. The embedded widget will automatically update with the latest information.
<iframe src="https://aimyflow.com/ai/polymerhq-io/embed" width="100%" height="400" frameborder="0"></iframe>
Explore Similar Tools
truthsystems
Truth Systems is a programmatic AI governance and unified compliance agent that helps organizations, especially legal teams and innovation leaders, monitor and block non-compliant AI use in real time across vendors through a browser extension and platform. For compliance, legal, and risk professionals, it can make AI oversight more actionable by embedding live guardrails, access controls, and audit trails directly into everyday work.
Variance
Variance is an AI risk intelligence platform that helps enterprises detect, investigate, and enforce against fraud, user-generated content violations, marketplace abuse, and other trust and safety risks, mainly for teams in content platforms, marketplaces, and financial services. For trust and safety, fraud, compliance, and security teams, it can speed real-time investigations and policy enforcement by connecting data streams and automating decisions across large volumes of activity.
Home | Veria Labs
Veria Labs is an AI-powered continuous pentesting platform that analyzes codebases and CI/CD workflows to find, validate, and suggest fixes for real application vulnerabilities, mainly for security and engineering teams in high-stakes industries. For AppSec, security engineers, and developers, it can bring offensive security testing closer to every pull request so issues are identified and remediated earlier in the software delivery process.
Premier Physical AI Security Platform & Outdoor Solutions | Alpha Vision | Free Trial
Alpha Vision is a physical AI security platform that uses AI agents and workflows to monitor outdoor sites, detect unsafe or unauthorized activity, deter trespassing, and search footage, mainly for security, safety, and operations teams in industries such as construction, education, retail, utilities, and commercial real estate. In AI-enabled security operations, it can help site managers, investigators, and safety leaders respond faster, review incidents more efficiently, and maintain broader coverage across large or distributed properties.
Autonomous AI Pentesting Platform | Maced AI
Maced AI is an autonomous AI penetration testing platform that helps engineering and security teams find, validate, and fix vulnerabilities across code, APIs, web apps, cloud, and infrastructure, while producing audit-ready reports for SOC 2 and ISO 27001 workflows. For security engineers, DevSecOps teams, and compliance-focused developers, it can shorten remediation cycles by turning validated findings into proof-of-exploit evidence and merge-ready fix guidance.
Mnemom — Prove What Your AI Agents Are Thinking
Mnemom is an AI governance and trust infrastructure platform that helps organizations prove, enforce, and audit what AI agents did and why with cryptographic verification, mainly for enterprise security, compliance, and engineering teams. For CISOs, compliance leaders, and AI platform teams, it can strengthen agent oversight by enabling pre-action policy enforcement and audit-ready evidence instead of relying only on after-the-fact logs.
Clearly AI
Clearly AI is an AI security and privacy review platform that automates threat modeling, design reviews, and risk triage to help security, privacy, and product teams ship software faster with better review coverage. In AI-assisted software delivery, it helps application security and privacy professionals focus human judgment on prioritized findings instead of repetitive document analysis and manual questionnaires.
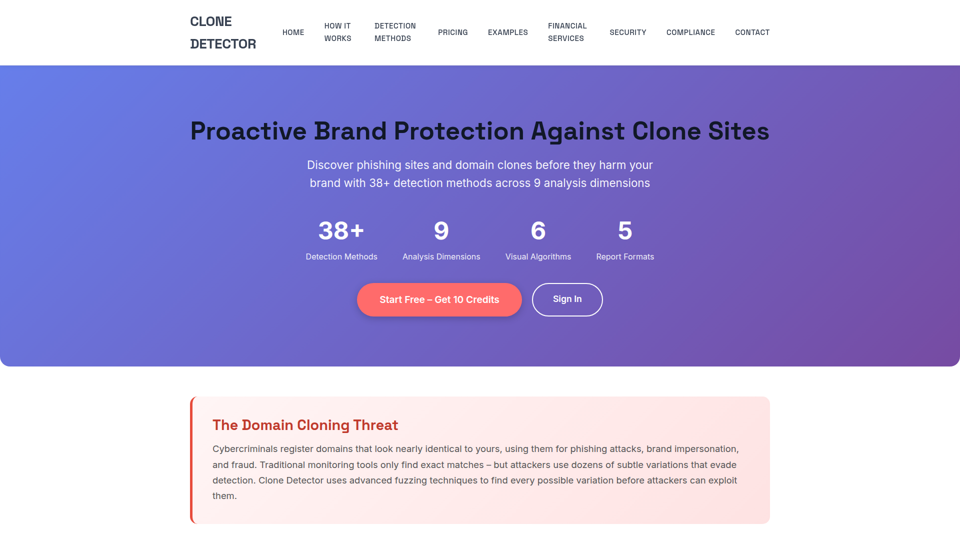
Clone Detector – Brand Protection & Phishing Site Detection Tool
Clone Detector is a brand protection and phishing site detection tool that helps businesses and security teams find fraudulent domain clones and lookalike websites using domain fuzzing, visual similarity analysis, and risk-based reporting. For cybersecurity, compliance, and brand protection roles, it can improve AI-era monitoring by surfacing subtle impersonation threats earlier and supporting faster investigation, reporting, and response.